Reading time: 2 min
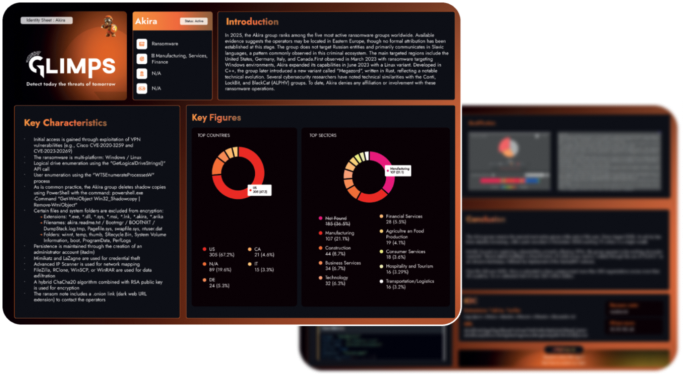
In 2025, the Akira group ranks among the five most active ransomware groups worldwide. Available evidence suggests the operators may be located in Eastern Europe, though no formal attribution has been established at this stage. The group does not target Russian entities and primarily communicates in Slavic languages, a pattern commonly observed in this criminal ecosystem.
The main targeted regions include the United States, Germany, Italy, and Canada. First observed in March 2023 with ransomware targeting Windows environments, Akira expanded its capabilities in June 2023 with a Linux variant. Developed in C++, the group later introduced a new variant called “Megazord”, written in Rust, reflecting a notable technical evolution. Several cybersecurity researchers have noted technical similarities with the Conti, LockBit, and BlackCat (ALPHV) groups. To date, Akira denies any affiliation or involvement with these ransomware operations.
Our Cyber Threat Intelligence analysts have compiled the available information into this profile:
- Context
- Operational mode
- IOCs
- Analysis results with GLIMPS Malware Expert