Secure file uploads in business applications
A booby-trapped resume in your applicant tracking system. A malicious invoice on your supplier portal. An infected receipt in your expense management app or customer portal. These files enter your IT environment through trusted, interconnected applications, and attackers know it.
Your business applications are a security blind spot
You’ve secured the usual attack vectors: email, endpoints, network. But what about those business applications that accept file uploads? They’re rarely within the SOC’s scope.
The issue isn’t the trust you place in your clients, partners, or candidates. The issue is that their files land directly on your servers, unscanned.
Those files are then stored, indexed, sometimes automatically opened by business processes. A malicious document can sit dormant for weeks before being accessed by an employee or triggered by a scheduled task.
Attackers know these paths. As traditional attack surfaces (email, networks…) face increasing scrutiny, they’re turning to these less guarded entry points.
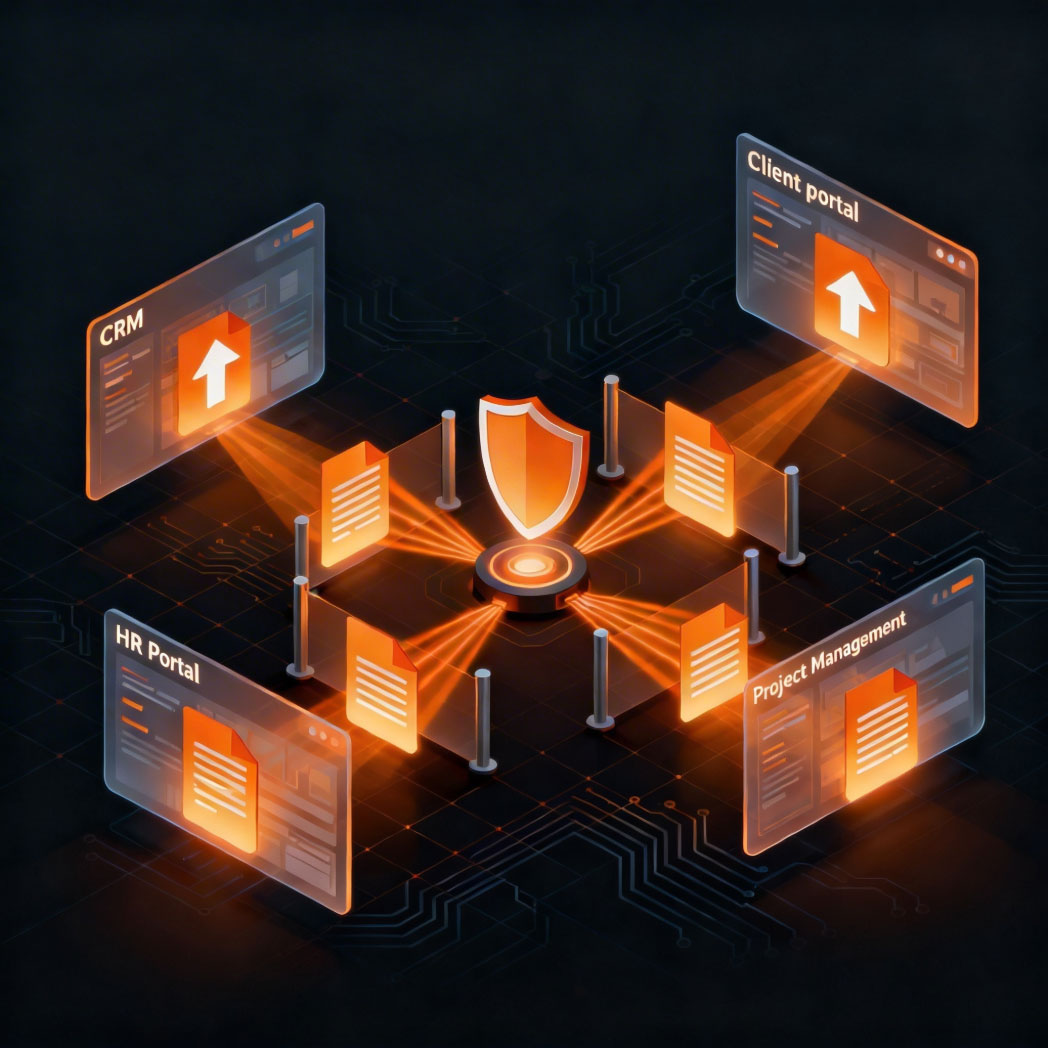
Your business applications receive files: who’s checking them?
Take stock. How many applications in your IT environment accept files from external sources?
On the customer side: document submission portals, contact forms with attachments… On the partner and supplier side: invoice submission platforms, RFP portals with supporting documents… On the candidate and employee side: job application platforms, resume databases, expense management apps with receipts, internal document management systems accessible to external contractors… On industry-specific workflows: claims management tools with photos and reports, regulatory filing portals…
Each of these applications is a potential entry point. And for each one, the question is: are files being analyzed before they’re stored, indexed, and processed?
How do you secure these flows without impacting your users?
That’s the question security teams face. Blocking critical business workflows is not an option and neither is asking IT teams to manually validate every file.
Your external users expect a seamless experience: upload files easily and receive immediate confirmation.
Your business teams need to receive the documents essential to their work, without being pulled into a validation process.
Security teams want visibility into these unmonitored flows, actionable alerts, and full traceability.
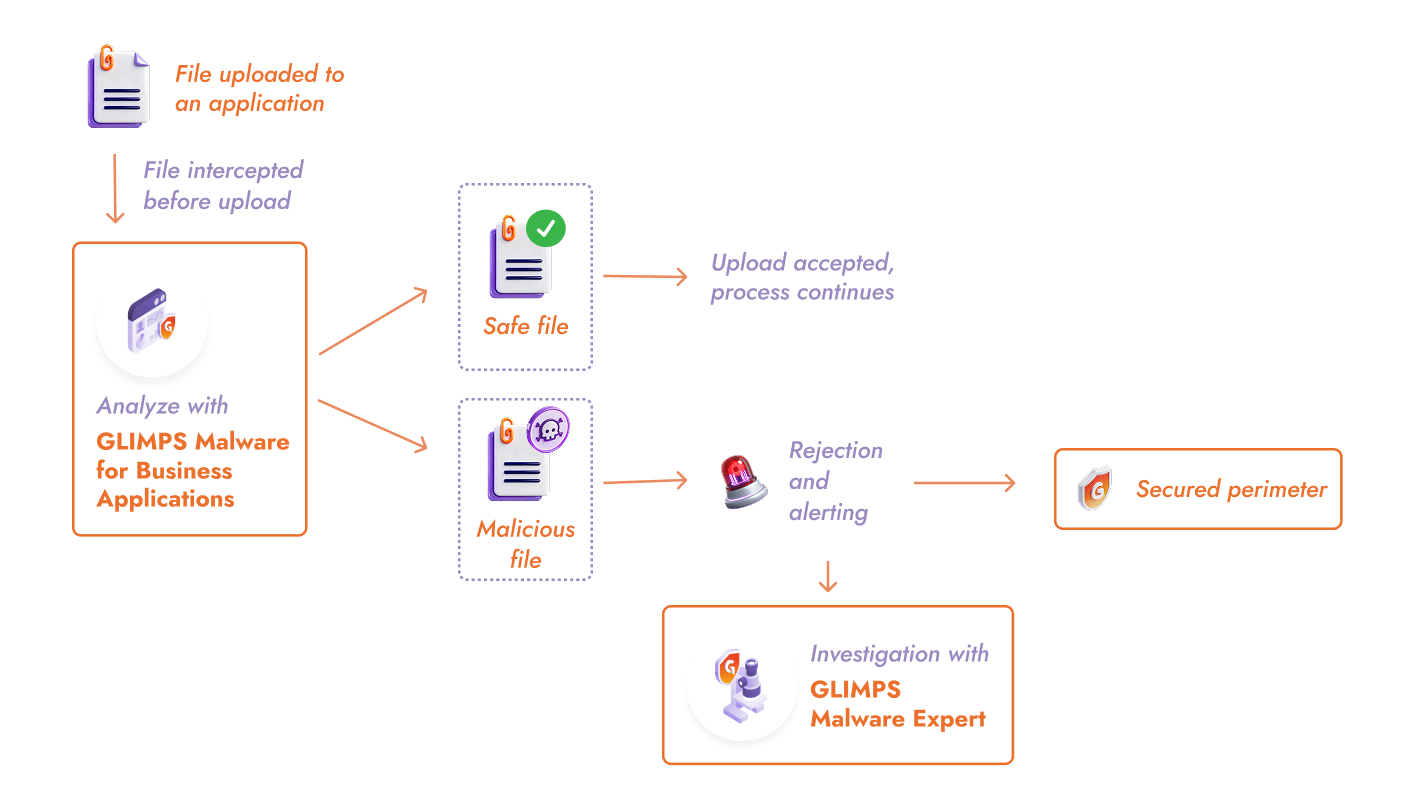
GLIMPS Malware for Business Applications integrates via REST API into your business applications. Integration is straightforward: a few lines of code to intercept the file at upload, send it for analysis, and retrieve the verdict.
Clean file? The upload proceeds normally. Malicious file? It can be automatically handled through SOAR integration, preventing execution or subsequent access and protecting your sensitive data. Security teams are notified through alerting with GLIMPS Malware Expert.
From upload to verdict: every file checked before it enters your environment
What you gain: a protected attack surface, uninterrupted operations
For the security team / CISO: You close a blind spot that was previously out of reach, with full visibility and the assurance of being alerted. Every protected application, every analyzed file, every blocked threat is logged. At your next audit or client security questionnaire, you can demonstrate that these entry points are covered.
For business teams: Their operations continue seamlessly. Clients submit their documents, candidates send their resumes, partners share their files. The difference: an invisible safety net intercepts threats before they reach your IT environment. Business teams are only alerted when action on their part is required.
For your clients, partners, and candidates: They notice no change. The upload takes a few seconds, just like before. But their data is better protected: an attacker won’t be able to use your portal as a vector to compromise your environment — and, by extension, access their information.
GLIMPS solutions to secure your business applications
GLIMPS Malware for Business Applications
The analysis layer for every incoming file:
- Integration via REST API or ICAP depending on your architecture
- Verdict in seconds, transparent to the user
- Configurable behavior: rejection, quarantine, notification
GLIMPS Malware Expert
Central investigation and file analysis platform:
- 25+ analysis engines (static, dynamic, AI)
- Automatic IOC and TTP extraction
- Secure document preview
- STIX, MISP, PDF, JSON export
- YARA editor and retrohunting
Day-to-day questions
Each application needs to be integrated into the analysis workflow. It’s very straightforward: a few lines of code to call the API at upload. Most development teams integrate an application in just a few hours.
No. Analysis takes a few seconds, which matches the typical processing time of an upload. The user sees their file “uploading,” then receives confirmation. They have no idea a security scan took place.
You define the behavior.
Option 1: the upload is rejected and the user receives an explanatory message (“your file could not be accepted”).
Option 2: the file is accepted but quarantined for manual review.
In both cases, your security team is alerted.
Files are analyzed on GLIMPS infrastructure (SaaS hosted in France) or on your own infrastructure (on-premise deployment). They can be automatically deleted after 24 hours or retained for the SOC (30 days by default). In both cases, they are never shared with third parties. GLIMPS is GDPR-compliant.
Protect your business applications against malware with GLIMPS
How many applications in your environment accept files from external sources? Let's assess together and find out how to secure them without disrupting your operations.
Request a demo