Analyze large file volumes
Enterprises accumulate terabytes of data across their file servers, but running security analysis at scale remains a major challenge. How do you scan millions of files without slowing down operations, while still catching the latest threats without compromising the confidentiality of your data?
Data volumes that exceed traditional tool capabilities
Enterprise storage infrastructures (NAS, SMB shares, file servers) host ever-growing volumes of data. Files pile up, and the threat they may pose is often overlooked. How can you be sure a malicious document isn’t sitting undetected in your environment?
Traditional antivirus solutions, designed for endpoint analysis, are not built to process millions of files per day. Scan times stretch out, server resources max out, and IT teams are forced to choose between security coverage and operational performance. The result: files go unscanned, and dormant threats proliferate.
Threats hide in the volume
Attackers exploit this weakness. A malicious file dropped into a shared directory can go undetected for weeks, enough time to spread silently. These directories often contain compressed archives (ZIP, RAR, 7Z) that serve as common attack vectors: they may hold dozens of nested files that traditional tools struggle to extract and analyze in depth.
Facing this reality, CISOs and storage administrators need a solution that can keep pace: scanning continuously, at high volume, without creating bottlenecks, all while maintaining strong detection against zero-day threats and variants.
The answer: massive-scale analysis with no trade-off on detection
Processing millions of files without sacrificing detection quality, that’s the balance GLIMPS Malware for Data Security delivers, combining industrial-grade throughput with analytical precision. Through the Host Connector, a lightweight agent installed on your Windows or Linux servers, your directories are monitored in real time. Every file added or modified is automatically submitted for analysis, with no manual intervention required.
The solution processes up to 2 million files per day, with an average analysis time of 3 seconds per file. Compressed archives are automatically extracted regardless of nesting depth, and each extracted file is analyzed individually. Files up to 100 MB are processed in full; beyond that, intelligent sampling techniques optimize response times without sacrificing detection effectiveness.
Unlike other solutions, particularly free ones, even the most sensitive and confidential files can be scanned. We do not have access to our customers’ data, nor do we use it.
This sustained throughput relies on 25 complementary detection engines, including around ten powered by artificial intelligence. The GLIMPS Deep Engine, based on code conceptualization, identifies zero-day malware and variants even when code has been modified, recompiled, or obfuscated.
Continuous and transparent monitoring: how does it work?
- Real-time monitoring: The Host Connector automatically detects any new file or modification within configured directories.
- Archive extraction: Compressed files (ZIP, RAR, 7Z, TAR, ISO, OVA…) are decompressed locally, regardless of nesting depth.
- Multi-engine analysis: Each file is submitted to all 25 GLIMPS detection engines, including the proprietary Deep Engine.
- Verdict and remediation: Malicious files are automatically quarantined; clean files continue their normal lifecycle.
- Centralized management: The Connector Manager lets you control all connectors, manage quarantine, and review activity logs.
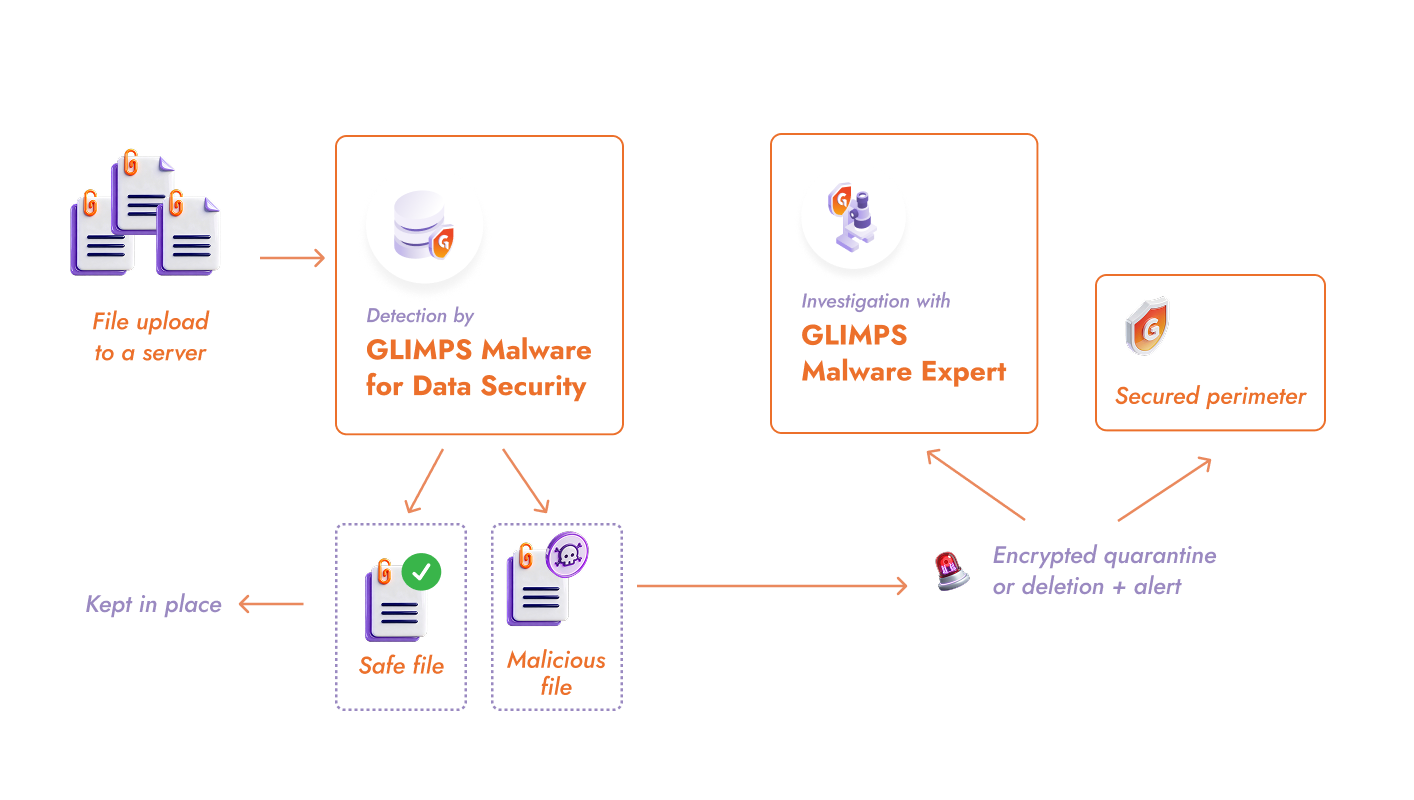
Analyze large file volumes with GLIMPS
GLIMPS Malware for Data Security
Analyze your files at scale, continuously:
- Real-time monitoring of storage environments
- High-volume processing
- Automatic extraction of compressed archives
- Automatic quarantine or removal of malicious files
GLIMPS Malware Expert
Central investigation platform for characterizing detected threats:
- Full visibility into analyzed files
- 25+ analysis engines (static, dynamic, AI)
- Automatic IOC and TTP extraction
- Secure document preview
- STIX, MISP, PDF, JSON export
Day-to-day questions
Our solutions offer advanced technical performance, are hosted in Europe and guarantee the confidentiality of the data analysed.
You can try GLIMPS Malware Expert for free on your files for 30 days.
For further information, please contact us.
No. Analysis runs in the background, completely transparent to end users. Employees continue to store and access their files as usual. Only files identified as malicious are quarantined before they can be opened.
The solution is designed to absorb activity spikes and scale alongside your infrastructure. Whether you go from a few hundred thousand to several million files, processing capacity adapts with no need to redesign your storage architecture.
Quarantined files remain accessible to administrators, who can review them, investigate the detection, and restore them if needed. This process prevents any data loss while maintaining perimeter security.
Yes. The solution is GDPR-compliant, helps meet NIS2 requirements, and can be deployed in sovereign environments (France/Europe hosting, SecNumCloud, on-premise). For the most sensitive contexts (critical infrastructure operators, Defense), dedicated configurations enable integration with multi-level sanitization gateways.
Analyze your files
Protect yourself from malware with GLIMPS, request a personalized demo
Request a demoAny other cybersecurity requirements?
Protect
Discover our suite of solutions designed for automatic malware detection across all your attack surfaces, offering you:
- a verdict that’s 3 seconds faster on average
- enhanced accuracy
- malware identification based on code
Investigate
Discover our solutions for in-depth threat analysis and incident response, which enable:
- enriched context to facilitate decision-making
- task automation
- advanced customization (YARA, data sets, and whitelists)

Engage your employees
Involve your employees in your company’s cybersecurity efforts and empower each employee toindependently verify the safety of suspicious files received via email, downloaded, or found on a USB drive
Control your data
Choose big data analytics and retroactive detection to secure your data. Continuously collect, store, and analyze your files using GLIMPS AI to ensure a secure, threat-free repository, today and tomorrow.
