GLIMPS Malware Expert
Advanced investigation console for SOC and CSIRT analysts with more than 25 detection engines, including a dozen AI-based engines, to qualify every threat in depth.
A complete platform to qualify and contextualize every threat
Exportable AI: protect your entire ecosystem
When the Deep Engine detects malware, it automatically generates a matching YARA rule. Export this rule to your EDR, SIEM, or NDR to spread GLIMPS detection across your ecosystem.
Immediate scope identification
Retrohunt and advanced search across your submission history reveal files related to a detected threat, even if they were submitted months ago.
From submission to verdict in seconds
GLIMPS Malware Expert centralizes all submissions coming from the full GLIMPS Malware product suite. Each file is analyzed by 25+ detection engines, including AI, combining static and dynamic analysis:
Static analysis (~3-second verdict): The file is submitted to Deep Learning engines (code conceptualization), Machine Learning (Windows PE, Linux ELF), a multi-script LLM (JavaScript, Python, PowerShell), antivirus engines, YARA rules managed by GLIMPS and applied automatically, as well as your own custom YARA rules. Verdict, malware family, and IOCs are available in seconds.
Dynamic analysis (CAPE sandbox): For threats requiring deeper investigation, the file is detonated in an isolated Windows environment. Execution screenshots are available for safe visualization. Hybrid analysis (static + dynamic) best qualifies the most sophisticated threats. Artifacts extracted during dynamic execution, including memory dumps, are automatically reanalyzed by the static engines for maximum coverage.
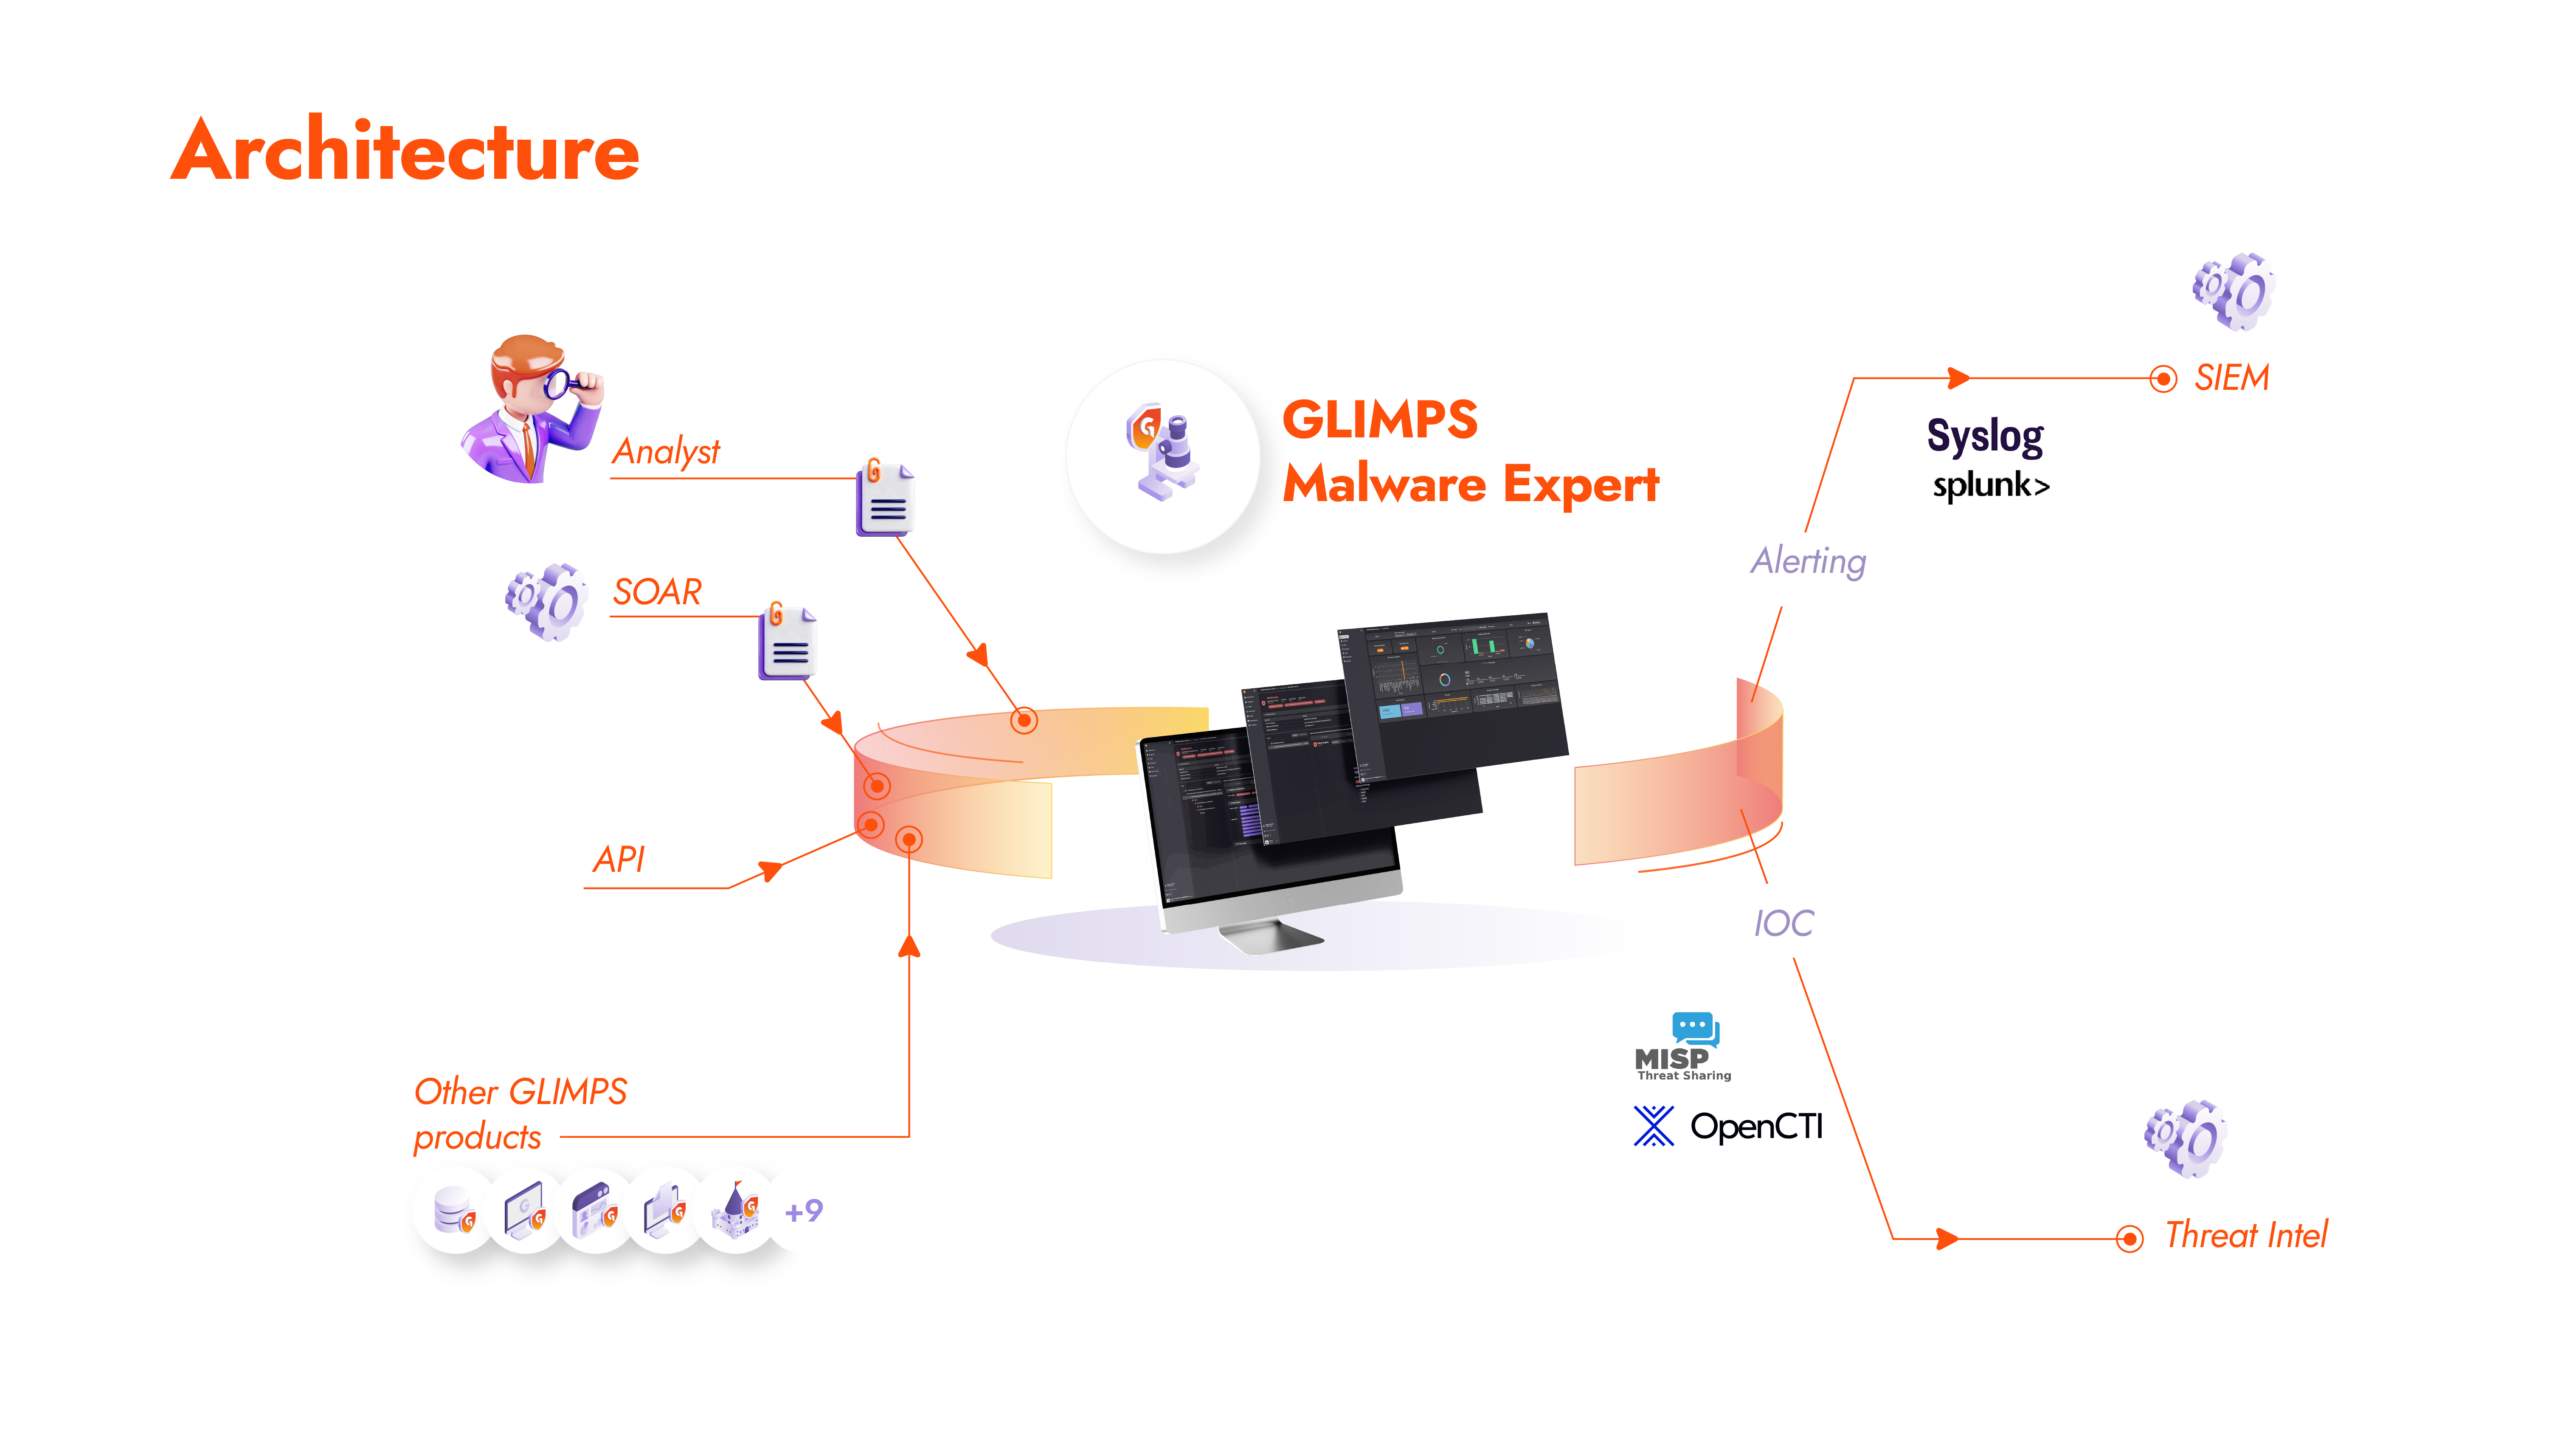
Context and export: MITRE ATT&CK mapping, IOC extraction, malware family attribution, automatic YARA rule generation. Results can be exported to your tools: native push to MISP, OpenCTI, Splunk, native SOAR connectors (SEKOIA.io, Cortex XSOAR, TheHive/Cortex) or via REST API and Python/Go libraries for your playbooks. Configurable alerts by email and SYSLOG.
Analyze, contextualize, export
Hybrid multi-engine analysis
More than 25 detection engines, including AI (Deep Learning, Machine Learning, multi-script LLM), plus antivirus engines, the customer’s YARA rules, and a CAPE sandbox. All file formats and programming languages are supported.
Retrohunt and threat hunting
Built-in YARA editor to create custom detection rules. Run retroactive searches across your full submission history to identify past compromises.
SOAR integrations and CTI exports
The GLIMPS Malware Expert API lets you integrate file scanning into SOAR playbooks via native connectors (SEKOIA.io, Cortex XSOAR, TheHive/Cortex) or via REST API and open-source Python and Go libraries. Native push to MISP, OpenCTI, and Splunk. Native EDR connectors: SentinelOne and HarfangLab. Configurable alerts: email, SYSLOG. PDF reports and JSON exports.
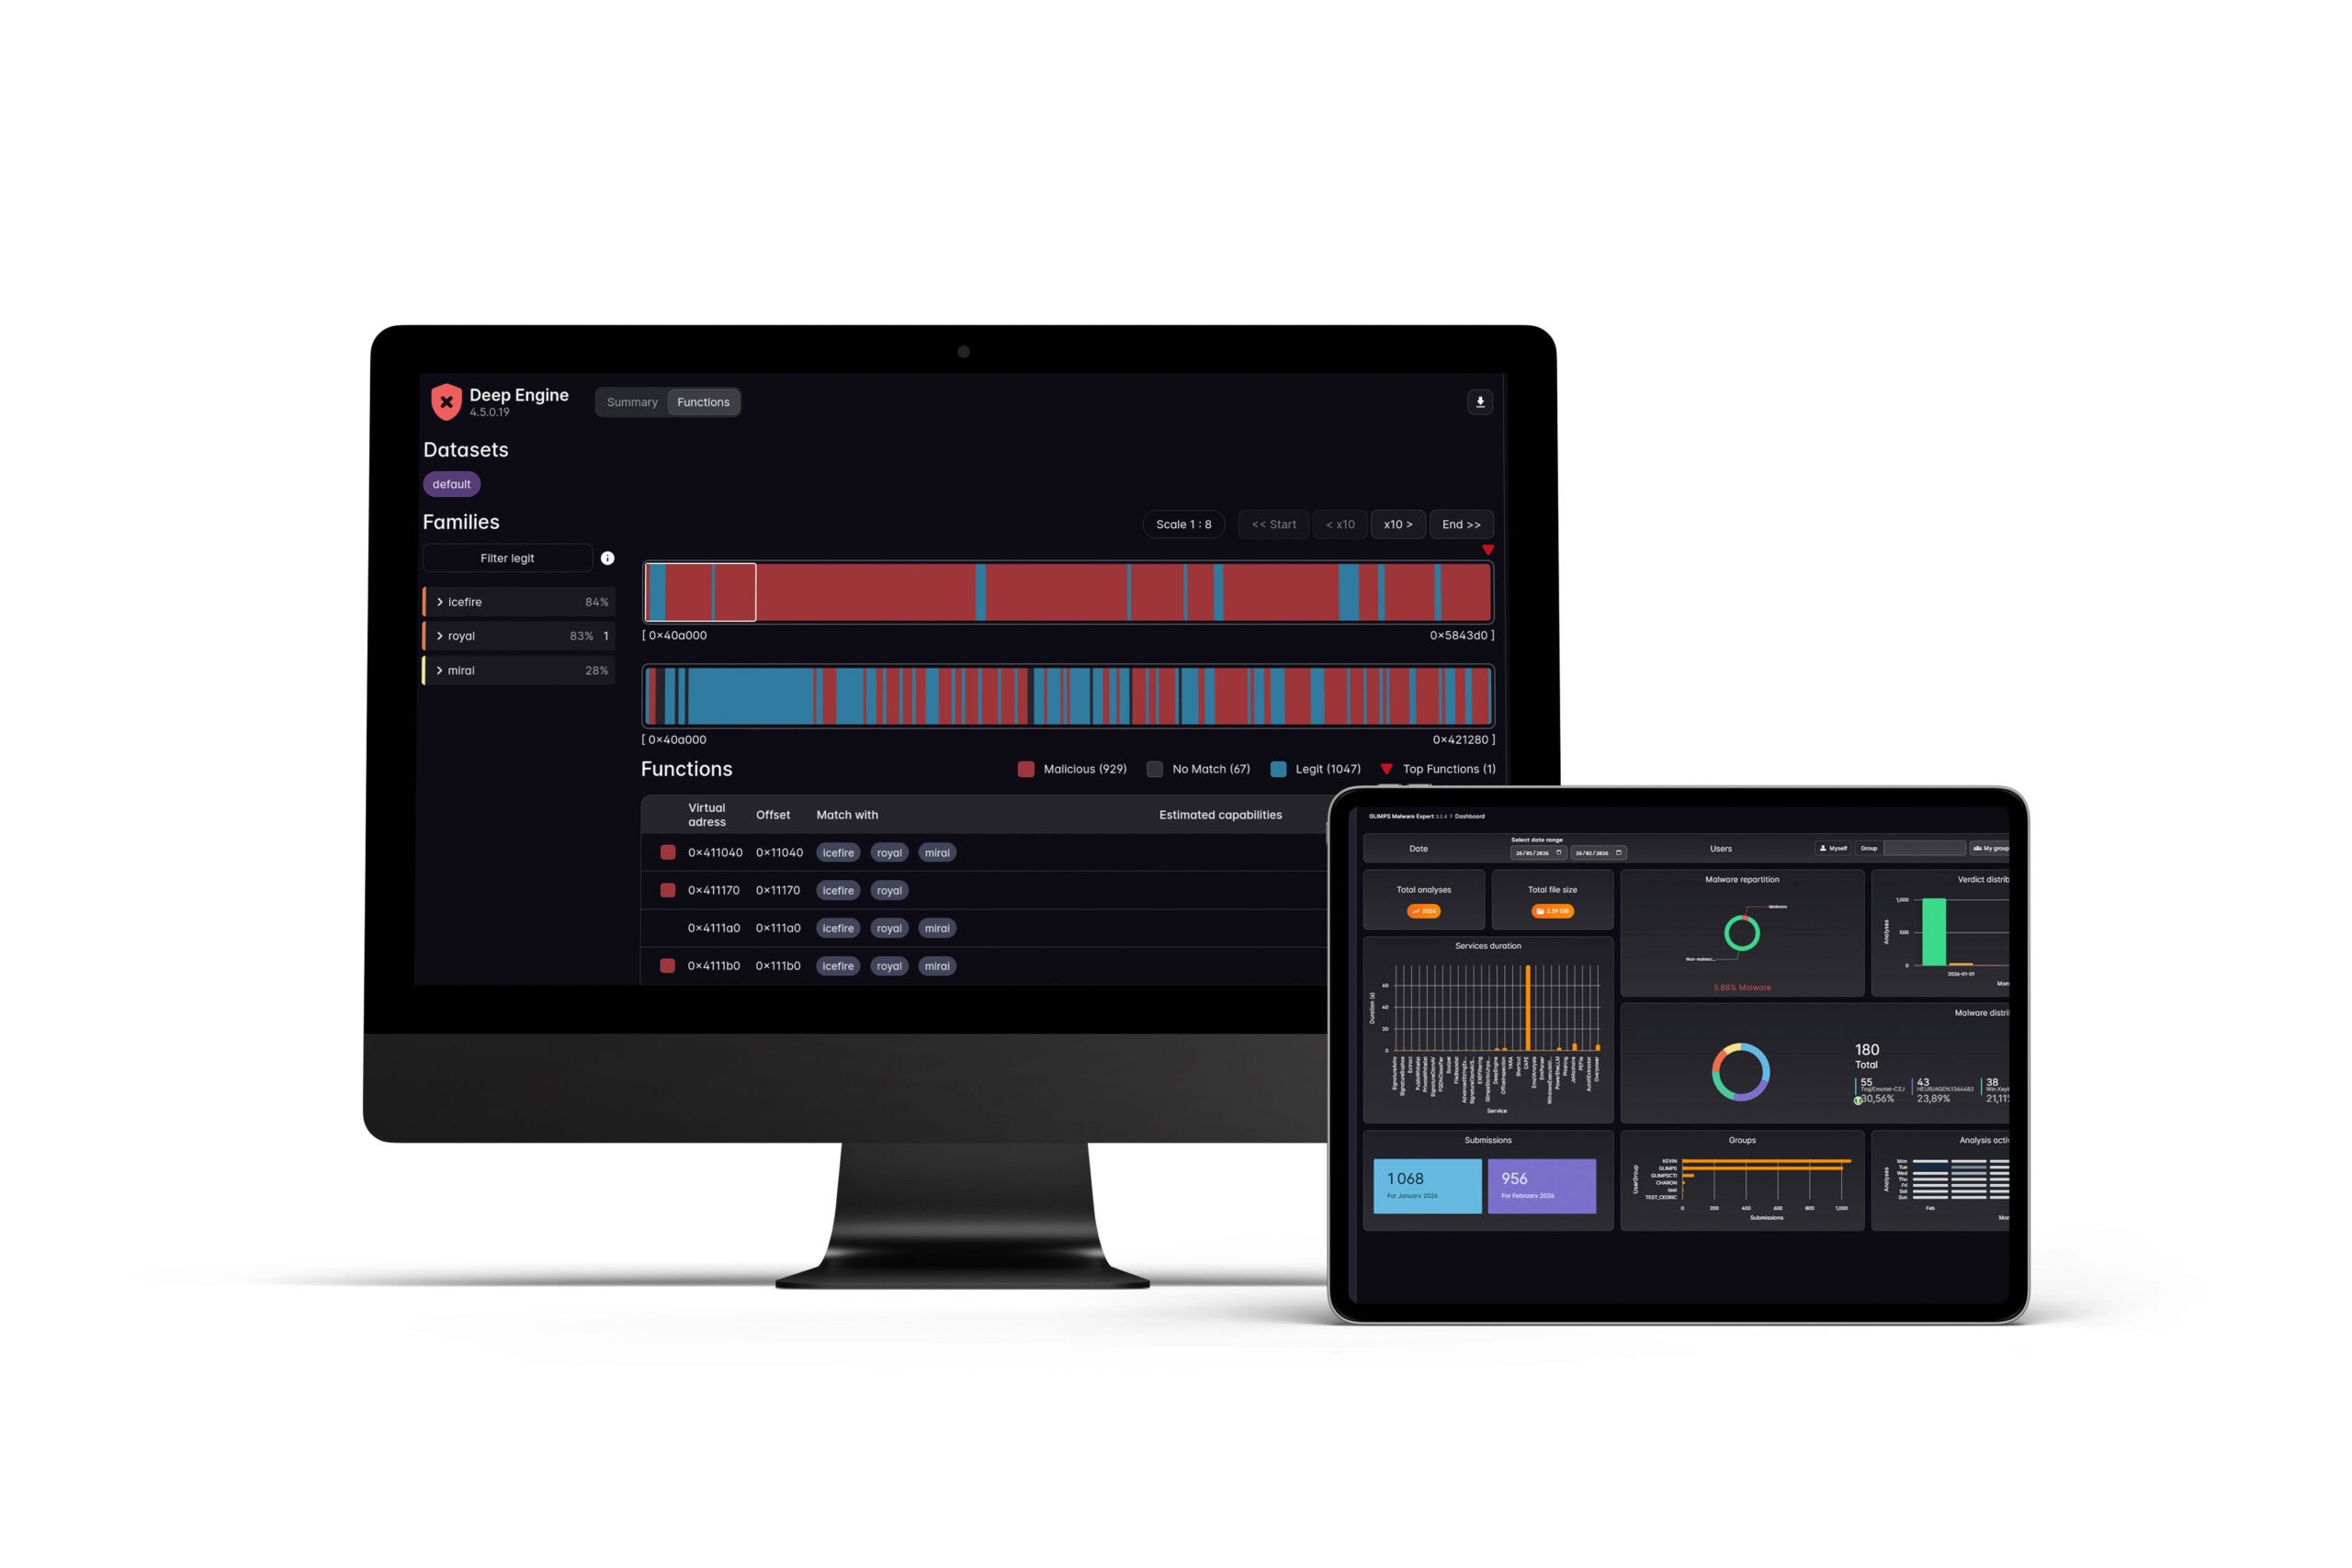
An optimized interface
GLIMPS Malware Expert, for whom?
Context: You handle hundreds of alerts every day and must quickly qualify suspicious files raised by your detection tools. The shortage of cyber talent and team turnover make it harder.
What GLIMPS Malware Expert brings: Deep analysis in seconds with static engines, complemented by the sandbox for complex cases. Automatic IOC extraction, MITRE ATT&CK mapping, and YARA generation accelerate every triage. Qualification time is cut by 3.
Context: During an incident, you need to understand the scope of compromise and reconstruct the attack chain quickly.
What GLIMPS Malware Expert brings: Retrohunt identifies all files related to the threat across your history. Code conceptualization correlation detects variants, even never seen before. Hybrid analysis (static + sandbox) qualifies the most sophisticated threats.
Context: You enrich your organization’s knowledge of threats and feed Threat Intelligence platforms.
What GLIMPS Malware Expert brings: Native push to MISP and OpenCTI, native SEKOIA.io integration, malware family attribution, and YARA generation to enrich reporting and proactively protect your ecosystem.
How customers use GLIMPS Malware Expert
Incident investigation and response (DFIR)
Analyze suspicious files collected during an incident. Hybrid analysis qualifies each file, extracts IOCs, and reconstructs the attack timeline with MITRE ATT&CK mapping. Automatically generated YARA rules are deployed on EDR to detect additional compromises.
Proactive threat hunting
Create your own YARA rules in the built-in editor and run retroactive searches across your history to detect dormant threats or previously unseen intrusions.
CTI enrichment
Automatically export IOCs and attributions to CTI platforms via native MISP and OpenCTI push. Each analysis enriches your knowledge base and improves your defensive posture. Native SEKOIA.io integration feeds your SOAR playbooks.
Why choose GLIMPS Malware Expert?
Code conceptualization technology
Code conceptualization technology, developed within the French Ministry of the Armed Forces by GLIMPS founders, detects zero-day threats, variants, and APTs that traditional signatures miss. Detection rate above 99%.
Exportable AI
YARA rules automatically generated by the Deep Engine can be exported to your EDR, SIEM, and NDR. GLIMPS detection spreads across your security ecosystem.
Sovereignty and confidentiality
French vendor, hosted in France and Europe. Unlike VirusTotal, your analyzed files are never shared or exposed. GDPR compliant and NIS2 aligned. Available as SaaS and On Premise with the same performance.
Used by the French Armed Forces
GLIMPS is labeled “Cybersecurity Made in Europe” and “Used by the French Armed Forces”. Winner of French Tech 2030, incubated by the French Ministry of the Armed Forces. GLIMPS is used by ANSSI for French government agents via https://jecliqueoupas.cyber.gouv.fr.
Frequently asked questions
GLIMPS Malware Expert provides a REST API and native connectors for leading platforms: native push to MISP, OpenCTI, and Splunk, native SOAR connectors (SEKOIA.io, Cortex XSOAR, TheHive/Cortex), and native EDR connectors (SentinelOne, HarfangLab). The REST API and open-source Python and Go libraries let you integrate file scans into any SOAR playbook. Alerts are configurable via email and SYSLOG. SaaS or On Premise deployment is done in a few hours without changing your existing infrastructure.
A sandbox only analyzes dynamic behavior, which usually takes several minutes. GLIMPS Malware Expert combines 25+ static engines (including Deep Learning on code) with a CAPE sandbox for dynamic analysis. The static verdict is available in ~3 seconds. Hybrid analysis detects evasive malware designed to bypass sandboxes, as well as variants never executed. Artifacts from dynamic execution, including memory dumps, are automatically reanalyzed by the static engines.
Yes. Data retention for files and analyses is fully configurable. In On Premise deployments, no data leaves your infrastructure. In SaaS, hosting is in France. NIS2 aligned.
When the Deep Engine detects malware through code conceptualization, it can automatically generate a matching YARA rule. The rule is immediately usable for retrohunt (searching within your history) and exportable to your EDR, SIEM, or NDR to protect your fleet. This is exportable AI: GLIMPS detection spreads across your ecosystem.
In addition to these automatically generated rules, GLIMPS Malware Expert allows you to apply a set of YARA rules managed by GLIMPS and maintained by our teams, which enhance detection with every scan without any action on your part, and lets you create your own rules in the built-in editor for threat hunting and your specific use cases. These three categories complement each other: sharing your detections with your other tools, enhancing native detection, and customizing detection to your specific context.
Three key differences: sovereignty (your files are never shared or exposed), depth of analysis (25+ engines including Deep Learning on code, not only signature aggregation), and operational integration (native CTI push, SOAR connectors, YARA generation, built-in retrohunt, native EDR connectors).
How to integrate GLIMPS Malware Expert into your environment?
Request a demo
Are you interested in our products? Contact our experts and discover the full power of our solution!
Request a demo