GLIMPS Malware Kiosk
A sovereign file analysis portal for all employees. Instant AI-driven triage, with no cybersecurity expertise required.
Turn every employee into a cybersecurity contributor
Drag-and-drop triage
Users drag a suspicious file or email into the portal, or use the GLIMPS button in Outlook. More than 25 detection engines, including AI-based engines, analyze it and return a clear verdict in seconds. No complex steps.
Clear verdict, no jargon
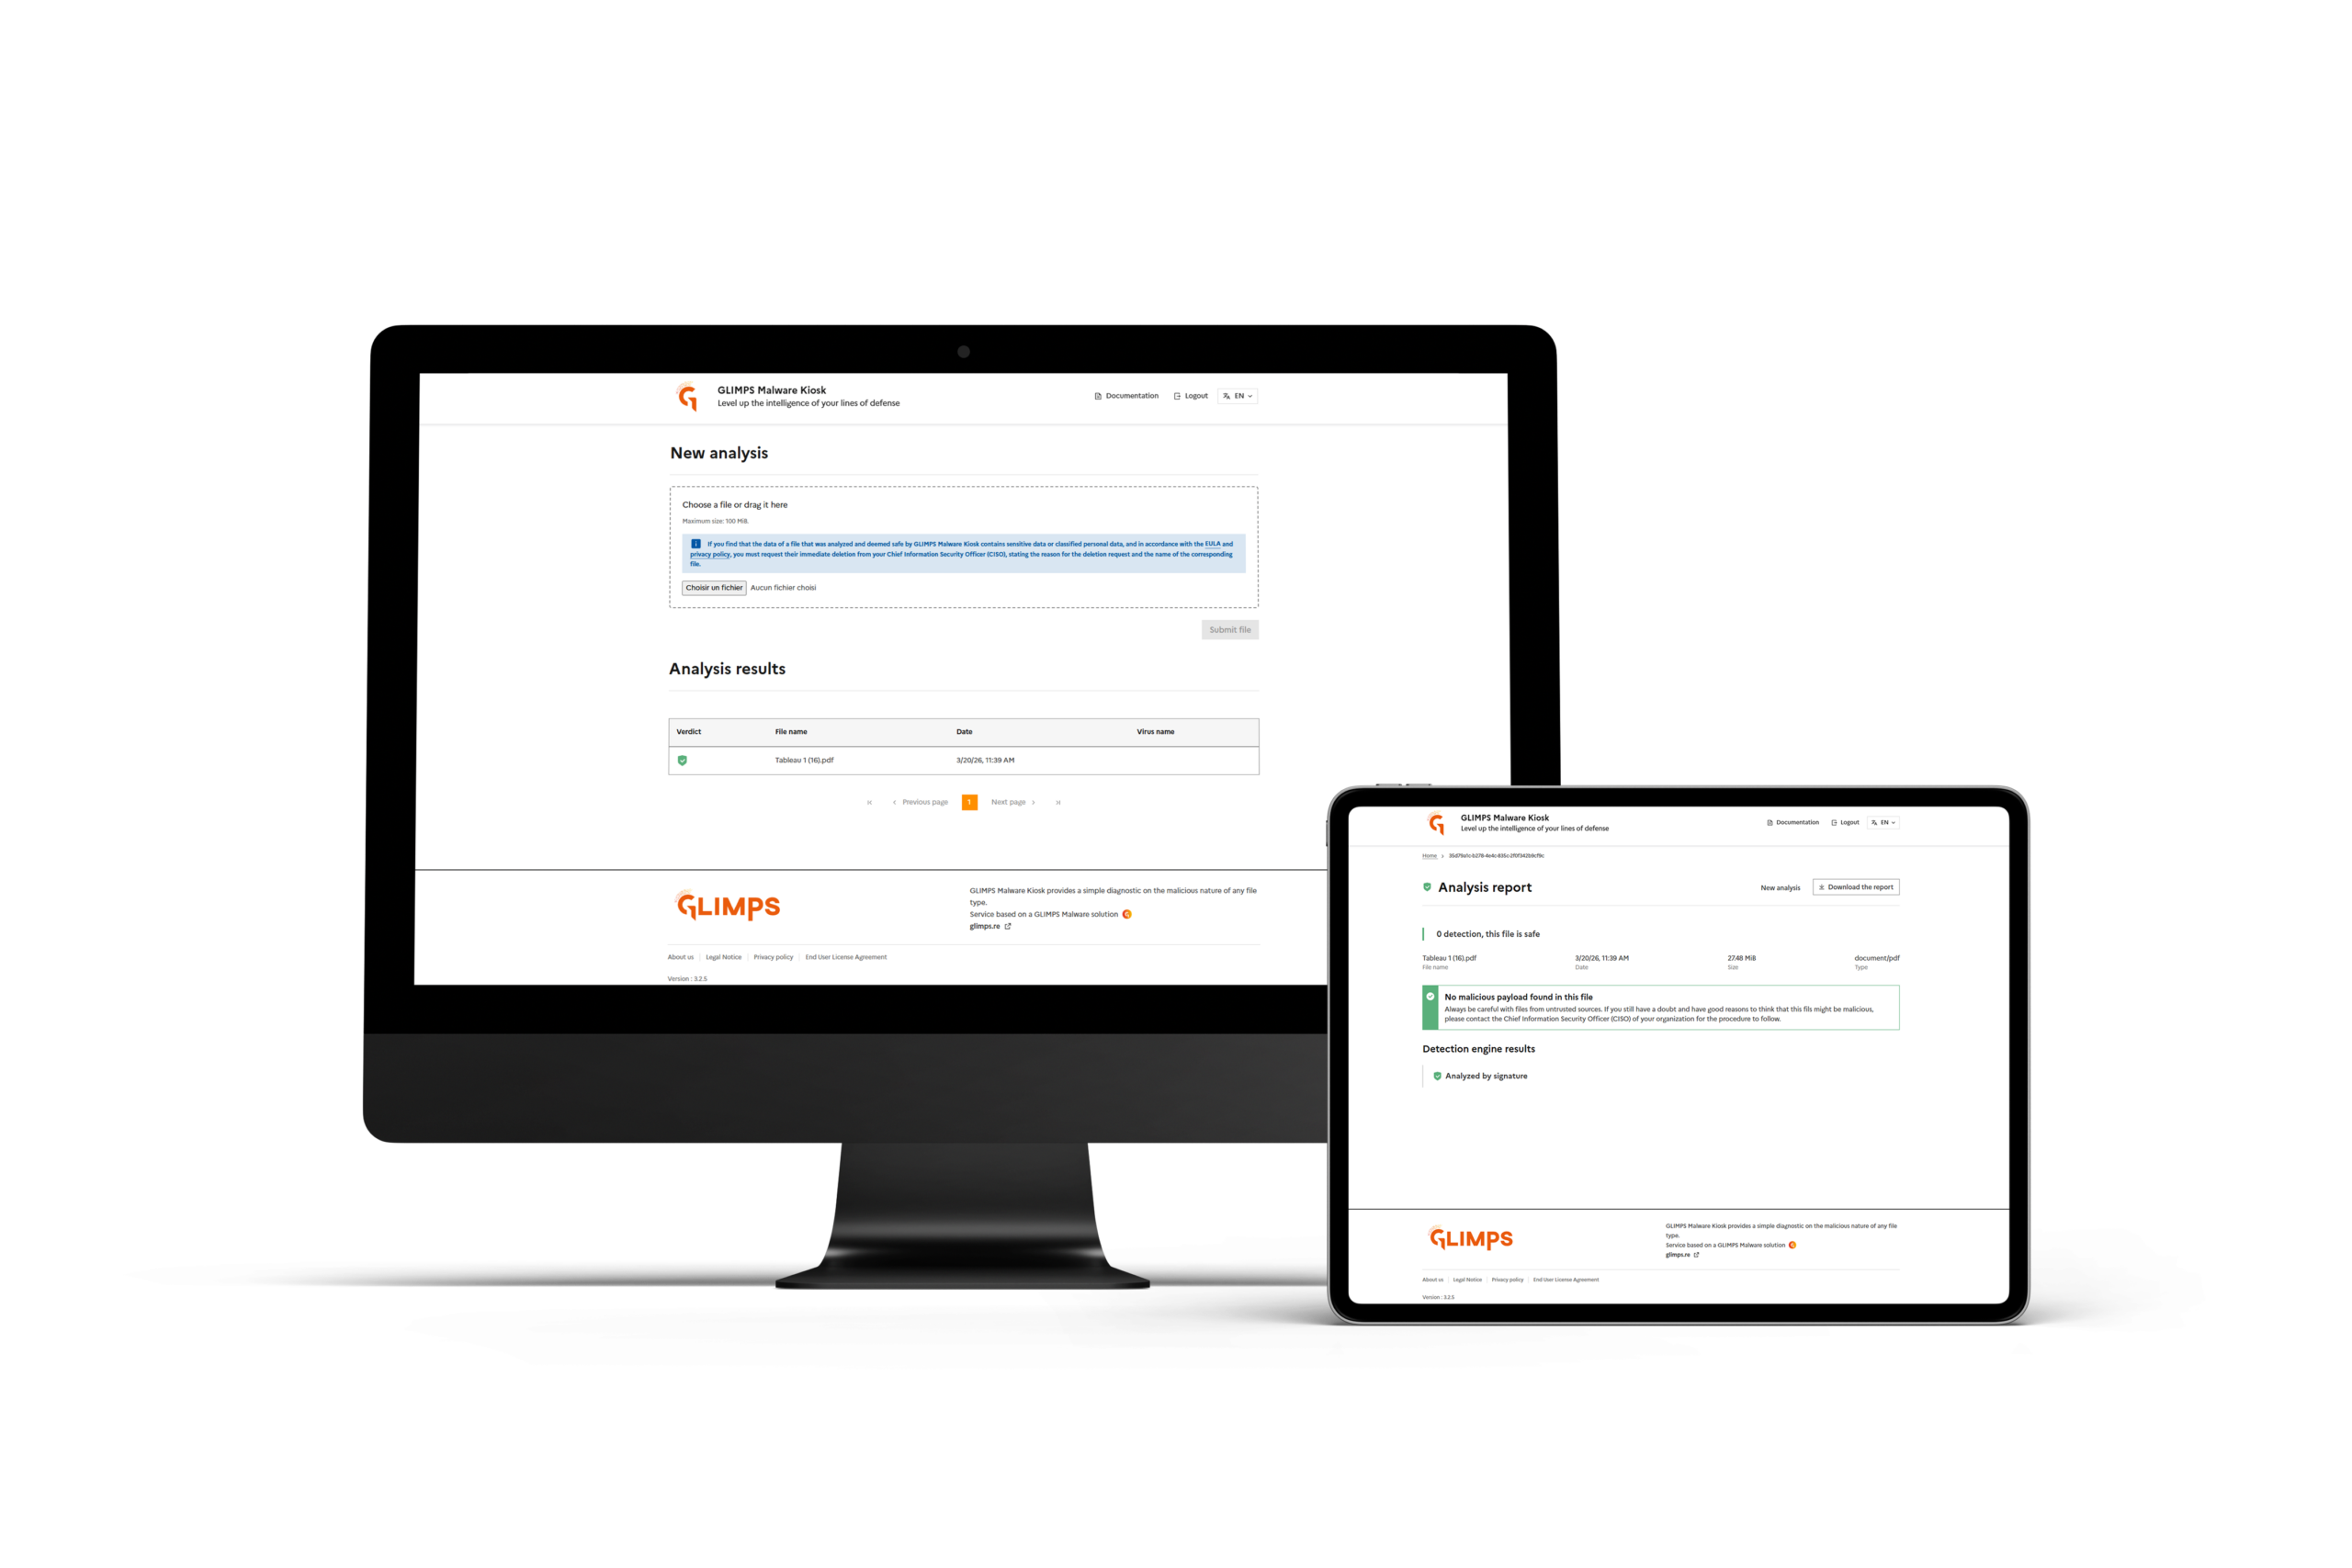
In seconds, the result is displayed as safe, suspicious, or malicious, along with the identified malware family. No interpretation needed. Users immediately know what to do.
Custom instructions when a threat is found
When a file is flagged as malicious, a customizable message explains what to do based on your internal procedures: delete, do not open, contact IT. Fewer support tickets and more autonomy.
An interface designed for user autonomy
A central drop zone, a progress indicator during analysis, and a color-coded verdict with the associated procedure message. The interface focuses on the essentials so any employee can use it from day one.
The portal can be branded to your company (logo, visual identity), and the messages displayed for malicious verdicts can be configured to match your procedures.
A detection report can be downloaded for each analysis, including the verdict, the identified malware family, and technical indicators.
“In the context of a public contract awarded to GLIMPS in 2022, ANSSI wanted to provide a service enabling government employees to check whether a work file is malicious while ensuring the analysis cannot be reused by commercial third parties. Under a simple appearance, the ‘Kiosk’ meets the needs of a wide audience with very different cyber skill levels.”
Key capabilities that make the difference
Deep multi-engine detection
More than 25 detection engines, including AI (Deep Learning, Machine Learning, LLM), plus antivirus engines and YARA rules. Supports Office, PDF, archives, executables, and scripts. Automatic recursive archive extraction.
Authentication and branding
Login based on your organization’s email domain. SSO compatible (SAML 2.0, OAuth 2.0). Customizable portal (logo, brand, procedure messages).
GLIMPS button in Outlook
Kiosk can also be deployed as a GLIMPS button directly integrated in Outlook. Employees submit a suspicious email with one click without leaving their mailbox.
GLIMPS Malware Kiosk, for whom?
Context: You receive a suspicious file by email, via USB, or through a sharing portal. You do not know if it is safe to open and you do not want to overload IT with a support ticket.
What GLIMPS Malware Kiosk brings: A one-click portal, a clear verdict in seconds, and precise instructions if a threat is detected. You become a cybersecurity contributor with no technical skills.
Context: You want to reduce attack surface by involving employees in threat detection while keeping visibility into suspicious files circulating in the organization.
What GLIMPS Malware Kiosk brings: A sovereign portal that turns every employee into an early warning source. Submissions feed GLIMPS Malware Expert for full visibility. GLIMPS code conceptualization technology detects threats traditional antivirus engines miss. GDPR compliant and NIS2 aligned.
Context: You deploy security tools and manage employee “is this safe?” requests.
What GLIMPS Malware Kiosk brings: Fewer support tickets thanks to user autonomy. Simple administration (branding, messages, retention, SSO auth) and usage metrics. All submissions are available in Expert for investigation when needed.
Context: You investigate detected threats and need to quickly qualify suspicious files reported by employees.
What GLIMPS Malware Kiosk brings: A Threat Intelligence signal fueled by spontaneous employee submissions. Each analyzed file is accessible in GLIMPS Malware Expert for deeper investigation, retrohunt, and correlation.
How customers use GLIMPS Malware Kiosk
Self-service triage for employees
An employee receives an unusual email attachment. They drag the file into GLIMPS Malware Kiosk and get a verdict in seconds. If malicious, the portal instructs them to delete it and contact IT. The SOC team receives an alert at the same time.
Sovereign protection for government employees
ANSSI uses GLIMPS Malware Kiosk via jecliqueoupas.cyber.gouv.fr to help government employees verify the safety of work files. The analysis is sovereign and cannot be reused by commercial third parties.
File analysis portal for multi-site organizations
A multi-site company deploys GLIMPS Malware Kiosk for all employees (500+ users). The portal is branded to the company. Submissions from all sites are centralized in GLIMPS Malware Expert for unified visibility.
Why choose GLIMPS Malware Kiosk?
Code conceptualization technology
Code conceptualization technology, developed within the French Ministry of the Armed Forces by GLIMPS founders, detects zero-day threats and variants that traditional antivirus engines miss. Detection rate above 99%. Employees get the same level of protection as SOC analysts.
Sovereignty and confidentiality
French vendor, hosted in France and Europe. Unlike VirusTotal, your analyzed files are never shared or exposed. GDPR compliant and NIS2 aligned. Available as SaaS and On Premise.
Used by the French Armed Forces and ANSSI
Incubated by the French Ministry of the Armed Forces, sed by the French Armed Forces and winner of French Tech 2030. GLIMPS is used by ANSSI for government employees via jecliqueoupas.cyber.gouv.fr.
Frequently asked questions
Two end-user deployment options are available: the web portal (URL access, no installation) or the GLIMPS button in Outlook (one-click email submission). On the infrastructure side, the solution is available as SaaS (portal URL provided, SSO configuration) or On Premise (Docker image or Helm chart).
Yes. Kiosk can be used standalone for end-user triage. However, adding Expert enables security teams to access deeper analysis, run retrohunt, and correlate threats across all attack surfaces.
Three key differences: sovereignty (your files are never shared or exposed), depth of detection (25+ engines including Deep Learning on code), and operational integration (GLIMPS Malware Expert for investigation, SIEM alerting, portal branding).
Request a demo
Are you interested in our products? Contact our experts and discover the full power of our solution!
Request a demo