GLIMPS Fortress
Organizations handle massive volumes of files on a daily basis: open-source components, third-party libraries, business binaries, and data from multiple sources. How can you ensure that these files do not contain hidden threats? How can you verify their integrity before integrating them into your CI/CD pipelines? And how can you detect a previously undetected compromise after the fact when a new malware signature is discovered?
A comprehensive data analytics platform with key features:
Analysis of large datasets without real-time constraints
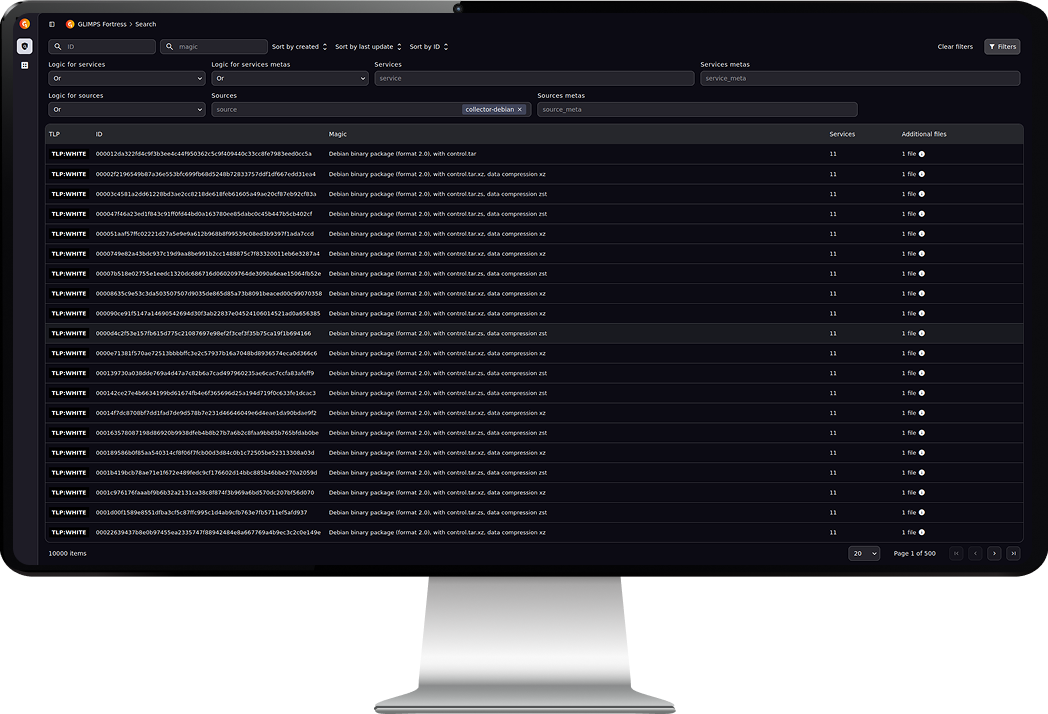
GLIMPS Fortress is a powerful tool designed to meet the demands of big data and analyze very large volumes of data.
Frequency of analysis
The data source can be queried periodically to re-examine the files and assess whether they are malicious, based on newly discovered rules or information, with retrohunting or alerts triggered in the event of a new detection.
Interconnectivity
The solution can be connected to public or private data sources to take advantage of its unique analytical capabilities.
It can automatically feed your Threat Intel using our MISP and OpenCTI connectors.
Benefits of GLIMPS Fortress
High-Volume Analysis & Continuous Enrichment
Analyze over 1 million files per day with no real-time constraints. Each file becomes a living object: metadata, verdicts, and history are constantly updated.
Retroactive Detection
A file that’s clean today may reveal its malicious nature tomorrow. Every new YARA rule or signature is automatically applied to your entire repository.
Interoperability
Native integration with your cyber ecosystem: MISP, S3, OpenCTI (coming soon)… through an open API.
Comprehensive Features to Master Your Data
Collection & Storage
|
Analysis & Detection
|
Exploitation & Export
|
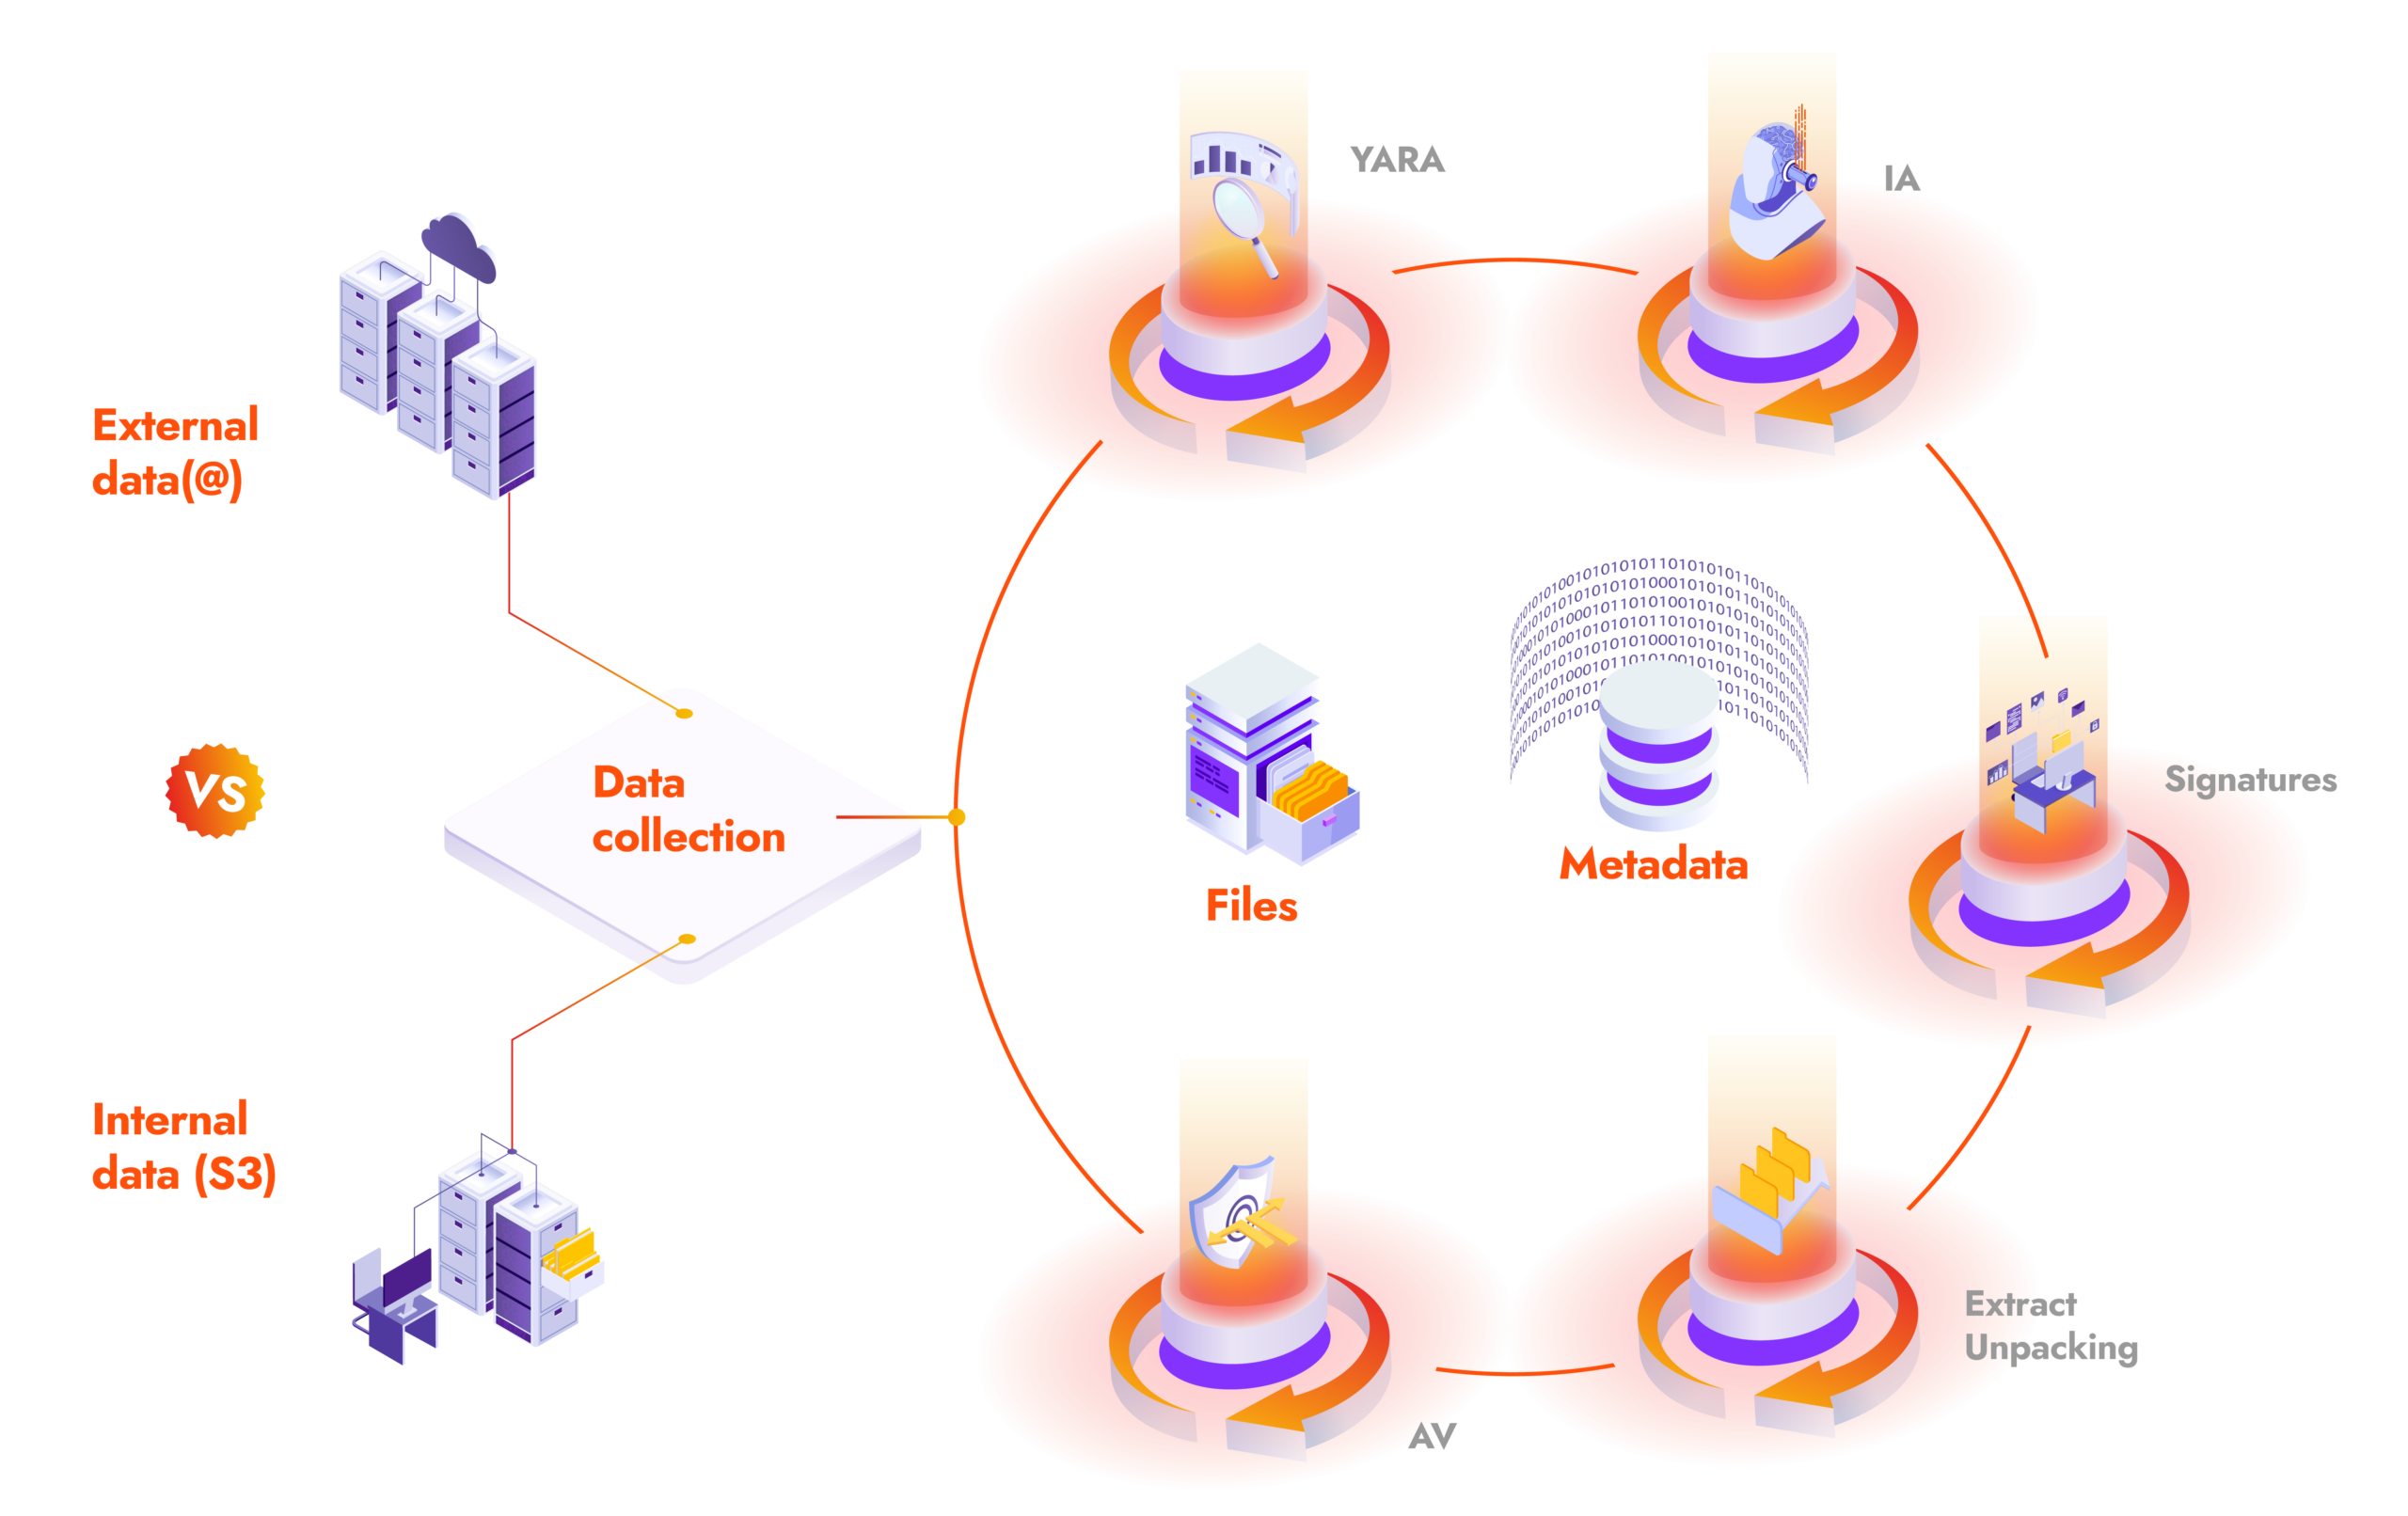
How does GLIMPS Fortress work? |
||
Who Is GLIMPS Fortress For?
| 1. Software Development Manager looking for security guarantees for your CI/CD pipeline and a trusted software repository capable of continuous analysis and retroactive threat detection. 2. SOC Manager |
3. CSIRT Manager looking to optimize incident response and system reconstruction through automated periodic file scans for iterative monitoring of compromised perimeters. 4. Big Data Manager |
Flexible Integration That Adapts to Your Infrastructure
- Connect to your sources: Configure your collectors in just a few clicks (S3 buckets, internal repositories, public sources)
- On-Premise deployment: Hosted in your infrastructure for complete data control
- Automated analysis: Your files are continuously analyzed by our 25+ engines with no manual intervention
- Export to your ecosystem: Native MISP connector available, OpenCTI coming soon, and open API to feed your existing tools
Why Choose GLIMPS Fortress?
Sovereignty
French vendor, On-Premise deployment, data hosted on your premises, 100% French support team.
Scalability
Kubernetes architecture designed to process over one million files per day.
Frequently Asked Questions
GLIMPS Fortress is an On-Premise solution deployed directly in your infrastructure. The architecture relies on Kubernetes, ensuring scalability and resilience. Our teams guide you through sizing (storage, processing capacity) and initial configuration. Once deployed, the instance is immediately operational and can scale progressively according to your needs. You maintain complete control of your data, which never leaves your environment.
GLIMPS Fortress connects to a wide variety of data sources. Private sources include S3 buckets and internal repositories. Public sources include open source repositories, MalwareBazaar, GitHub, Docker Hub, and OS repositories. The solution includes configurable collectors that automatically retrieve files from the sources you define. Two operating modes are available: duplicate data in the Fortress repository, or keep only metadata in the database while leaving files in your S3. This flexibility lets you build a comprehensive repository while controlling storage costs.
Retrohunting is a key feature of GLIMPS Fortress. When a new detection rule is added—whether a YARA rule, new antivirus signature, or updated AI model—it is automatically applied to all files already in the repository. If a new detection occurs, you are automatically alerted. This “digital cold case” approach enables you to hunt dormant threats and identify previously unnoticed compromises after the fact.
GLIMPS Fortress is designed to process massive file volumes. The platform can analyze over one million files per day thanks to its Kubernetes architecture that ensures scalability. Sizing is adjusted to your needs: storage, processing capacity, and reanalysis frequency are all configurable. Internally, GLIMPS operates Fortress with a repository of over 315 million files—proof of the solution’s robustness when handling very large volumes.
GLIMPS Fortress lets you create a trusted software repository for your development teams. The principle: mirror your APT package repositories in your Fortress instance. Each component is analyzed by our 25+ engines before being made available. Your developers access only validated packages free of malicious code. If a new threat is detected retroactively through retrohunting, you are immediately alerted. This approach integrates naturally into a DevSecOps workflow and secures your entire CI/CD pipeline.
GLIMPS Fortress includes native connectors with leading Threat Intelligence platforms: MISP (available now) and OpenCTI (coming soon). Indicators of compromise (IOCs) extracted by Fortress (hashes, signatures, behaviors) can automatically feed your knowledge bases. An open API also enables Fortress integration with your existing workflows and lets you query the repository from your analysis tools. Integration with SIEM/SOAR solutions is planned for future releases, enabling even greater automation of your detection and response chain.
Reanalysis frequency is fully configurable according to your needs. GLIMPS Fortress can rerun analyses every 4 to 5 hours, or at longer intervals: 24h, 48h, or several weeks. The cadence can vary by context: a CI/CD pipeline may favor frequent analysis, while an archival repository might opt for weekly scans. With each reanalysis, files benefit from the latest detection rules and AI engines, ensuring constantly up-to-date protection.
Currently, GLIMPS Fortress includes YARA rules developed by GLIMPS. Custom rule support will soon be available through two mechanisms: connecting to a GitHub repository containing your own YARA rules with automatic loading into the solution, or direct entry via a dedicated interface. Your custom rules can then be used for both retrohunting on existing files and automatic tagging of newly collected files. This evolution will enable CTI and SOC teams to detect context-specific threats directly from Fortress.
Secure Your Files at Scale with GLIMPS Fortress
Ready to see our solution in action? Talk to our experts today
Request a demo