GLIMPS Malware for Business Applications
Secure file transfers in your business applications with real-time AI detection, without changing your applications.
Stop malware before it reaches your information system
Detection before compromise
Every file uploaded by your users or partners is analyzed by more than 25 detection engines, including around ten AI-based engines, before entering your information system.
Integration in a few lines of code
A documented REST API and open source Python and Go libraries to integrate analysis into your applications in minutes.
No application changes
With our partner UBIKA (WAAP), analysis is performed upstream via reverse proxy. Your web applications remain unchanged.
Verdict in under 3 seconds
Instant analysis of files, including archives. Processing time compatible with file upload user experience, with no noticeable latency.
How does GLIMPS protect your business applications?
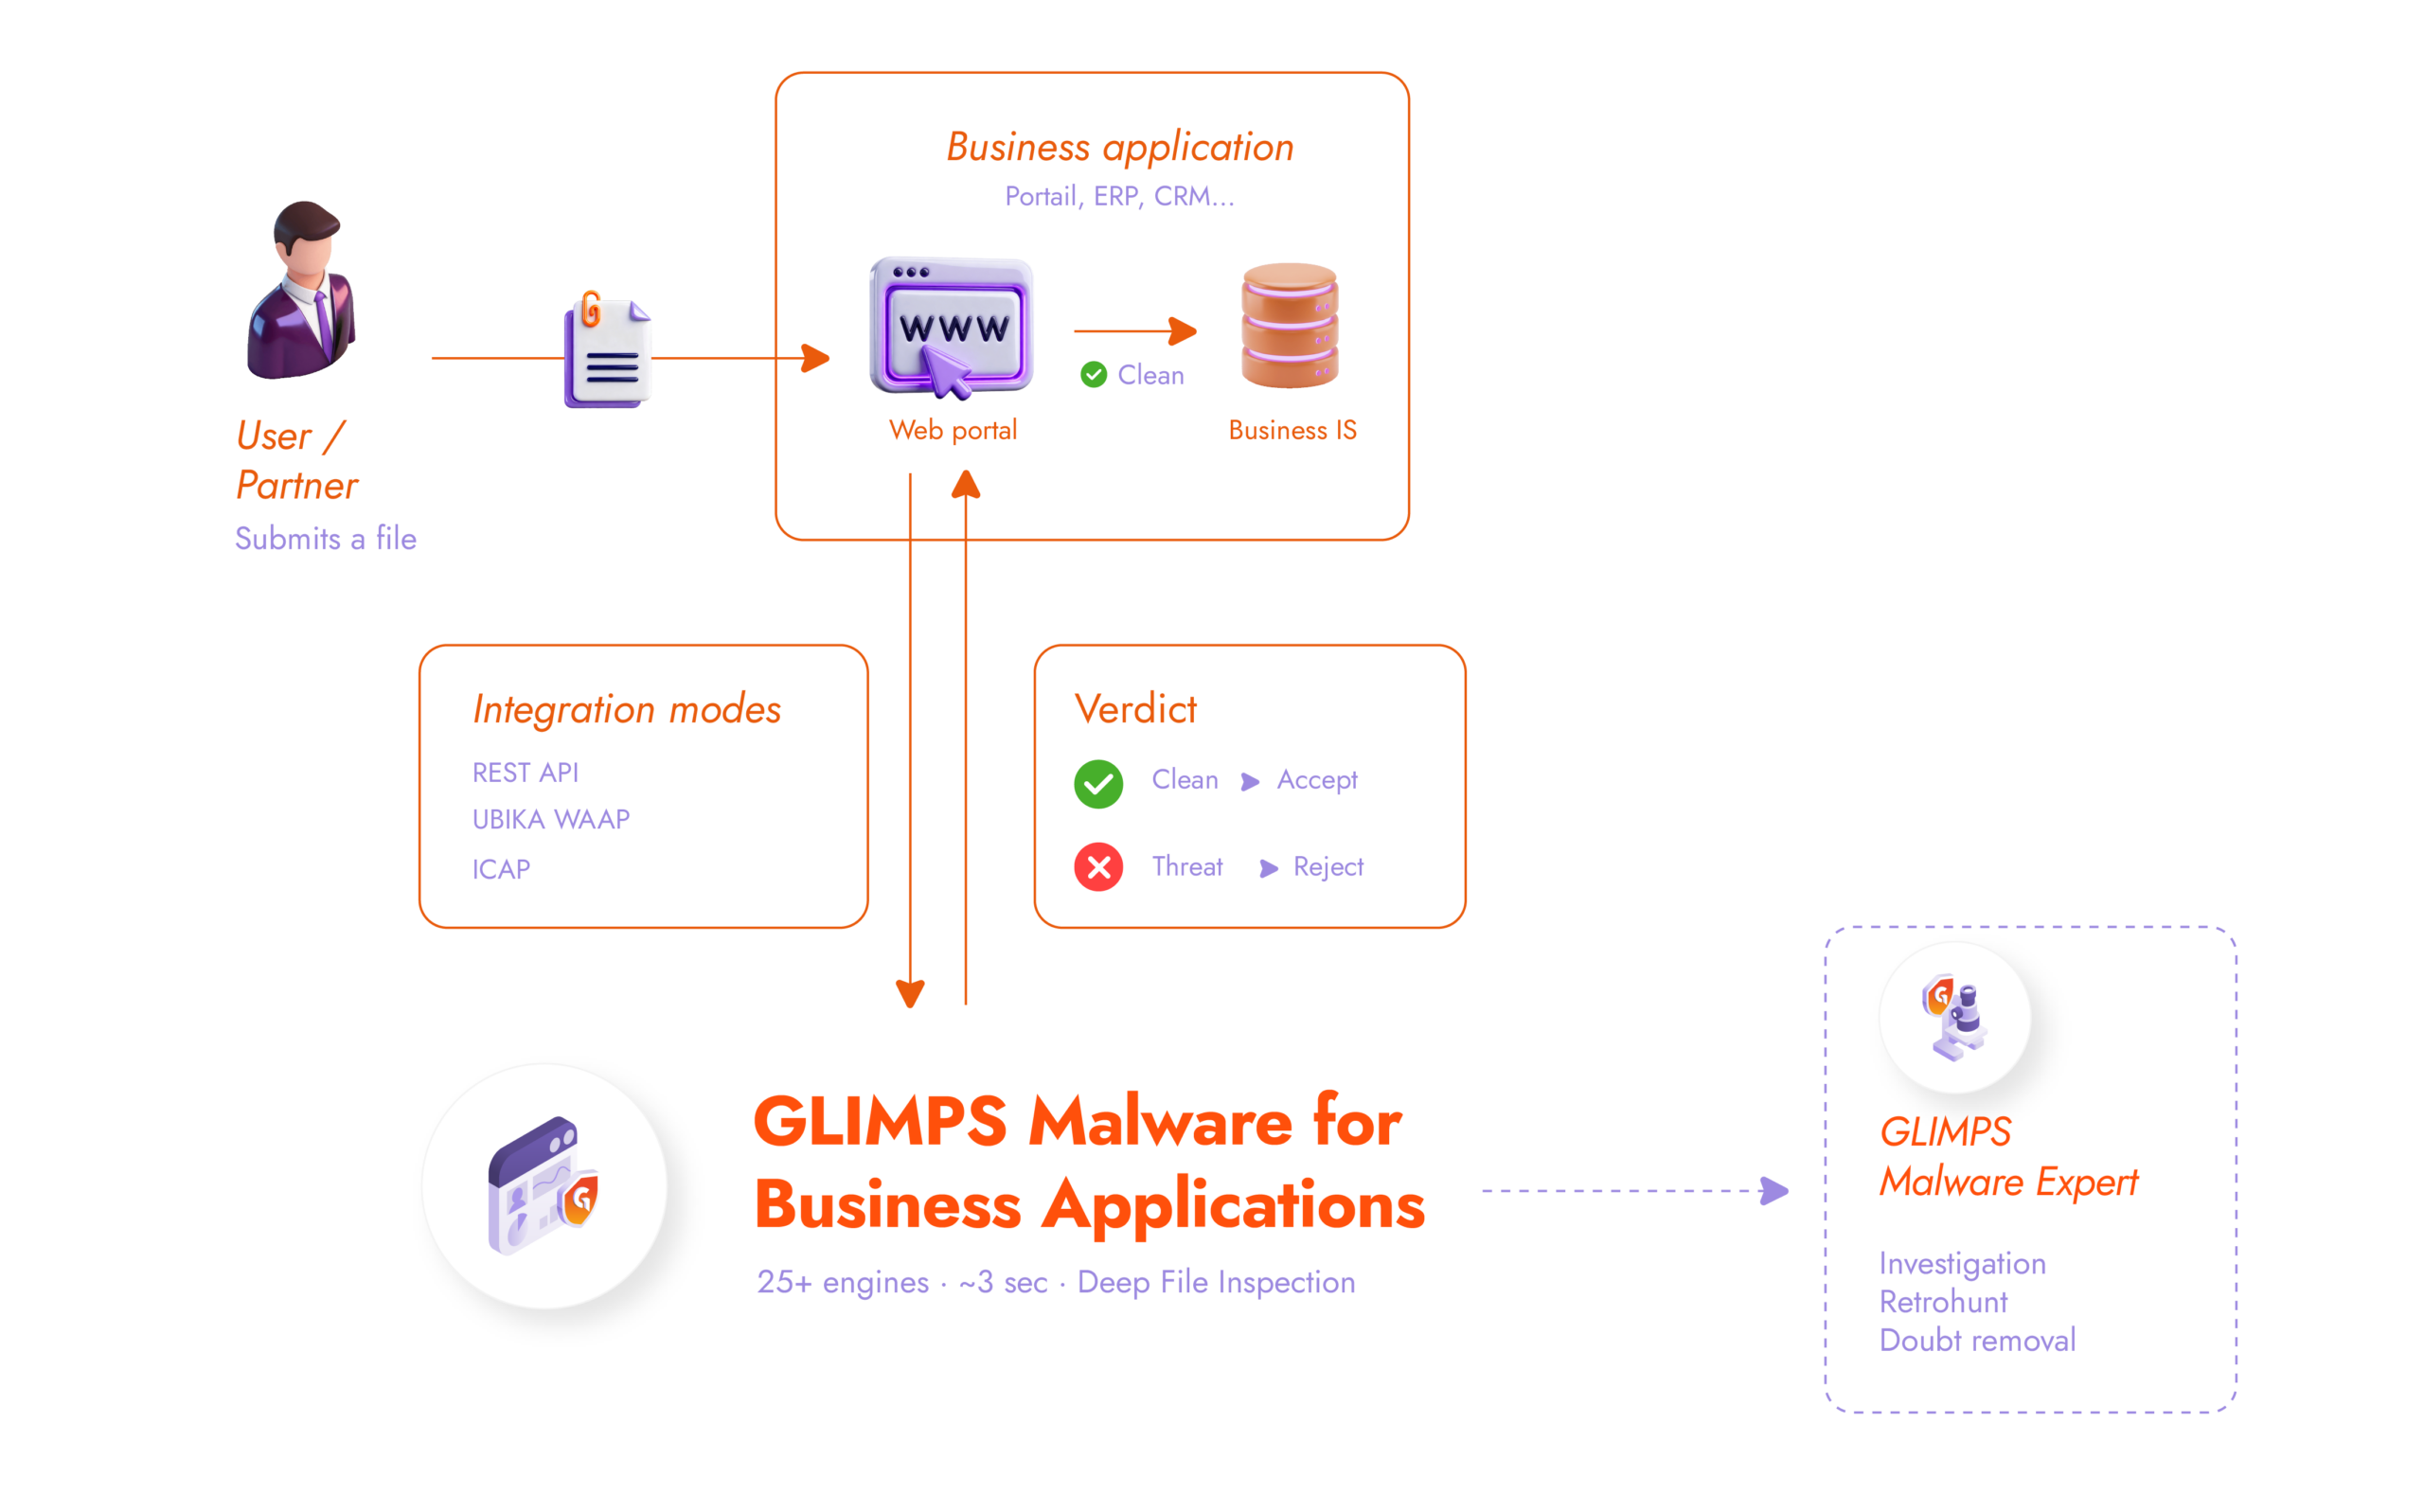
GLIMPS Malware for Business Applications sits between your users and your applications to analyze every file in transit before it enters your trusted environment:
GLIMPS Malware REST API: Your application submits each received file to the GLIMPS Malware API and applies an action based on the verdict: accept, reject, alert. Archives are automatically extracted and analyzed by GLIMPS. Open source libraries in Python and Go make integration easier and speed up connector development. ICAP integration is also available for compatible applications.
UBIKA WAAP integration: For protection without development, the connector developed by UBIKA (WAAP CSPN-certified by ANSSI) analyzes files in transit through its reverse proxy before they reach the application. No change to your web applications is required. Malicious files are blocked upstream, fully transparently.
All analysis results are centralized and available in GLIMPS Malware Expert for deep investigation, triage, and retrohunt.
Analysis capabilities built for your applications
Multi-engine detection
More than 25 detection engines, including around ten AI-based engines (Deep Learning, Machine Learning, LLM), complemented by antivirus engines and your own YARA rules, characterize every submitted file. All formats are supported.
Cache and performance
Built-in caching prevents resubmission of files already analyzed. Statistics dashboard on performed analyses.
GLIMPS Malware for Business Applications: who is it for?
Context: You develop or maintain business applications that receive files from users or external partners.
What GLIMPS delivers: A REST API that is easy to integrate, with ready-to-use Python and Go libraries. In a few lines of code, every uploaded file is analyzed before your application processes it.
Context: Your business applications are often an under-protected attack surface, exposed to threats carried by inbound files.
What GLIMPS delivers: A sovereign AI detection layer integrated upstream of your applications, drastically reducing the risk of compromise via malicious files. Aligned with GDPR and NIS2.
Context: You design your organization’s security architecture and must protect application flows without impacting performance.
What GLIMPS delivers: Flexible integration via REST API, open source libraries, or UBIKA reverse proxy, compatible with SaaS, on-premise, and hybrid environments, without redesigning your infrastructure.
How customers use GLIMPS Malware for Business Applications
Securing file upload portals
A bank or insurer receives supporting documents, IDs, and client documents through an online portal. Each file is analyzed by GLIMPS before entering the information system, eliminating the risk of compromise through a malicious attachment.
Protecting file exchanges with third parties
A services company receives hundreds of CVs, supplier documents, or tenders every day. GLIMPS automatically analyzes every file in transit and blocks threats before internal teams are impacted.
Why choose GLIMPS Malware for Business Applications?
Proprietary AI detection
GLIMPS’ code conceptualization technology, developed within the French Ministry of the Armed Forces by GLIMPS’ founders, identifies zero-day threats and variants that traditional antivirus solutions do not detect. Detection rate above 99%.
Sovereignty and compliance
French vendor, hosting in France and Europe, no data leaves the platform. Aligned with GDPR, compatible with NIS2 and PCI DSS.
Fast integration, low friction
Documented REST API, open source Python and Go libraries, and UBIKA partnership for protection without development. Operational within hours.
Used by the French Armed Forces
Used by the French Armed Forces”, incubated by the French Ministry of the Armed Forces and French Tech 2030 award winner.
Frequently asked questions
Integration is done through the GLIMPS Malware REST API. Open source Python (py-gdetect) and Go (go-gdetect) libraries are available on GitHub to speed up development. If you do not want to develop, the UBIKA integration protects your web applications via reverse proxy without any application changes. ICAP integration is also available for compatible applications.
Yes. GLIMPS Malware for Business Applications is available as SaaS (hosted in France), on-premise, and in SecNumCloud environments. Performance and capabilities are identical regardless of deployment mode.
Analysis is performed in under 3 seconds, compatible with file upload user experience. A caching system prevents resubmission. The API call is asynchronous: your application can keep running while analysis is in progress and retrieve the verdict as soon as it is available.
Traditional antivirus solutions rely on known signatures and do not detect zero-day threats or variants. GLIMPS combines more than 25 detection engines, including Deep Learning and Machine Learning, to characterize unknown threats with a detection rate above 99%.
Request a demo
Are you interested in our products? Contact our experts and discover the full power of our solution!
Request a demo